 easywall
GitHub ↗
Your firewall.
Your rules.
No surprises.
easywall is a web interface for the Linux nftables firewall. Every apply reverts itself after 120 seconds unless you confirm it — so editing your firewall over the network can never cut you off. Runs on a home server, a Raspberry Pi, or a rented VPS.
Debian / Ubuntu
sudo dpkg -i easywall_amd64.deb
amd64 and arm64, one package, a systemd unit and HTTPS built in.
Install →Docker
docker compose up -d
Lives in its own nftables table and touches nothing else on the host.
Run it →From source
make build && sudo make install
Go 1.27, no runtime dependencies beyond the kernel.
Build it →A firewall you keep your hands on
Everything lives on your own box: ports TCP/UDP, blocklist and allowlist, port forwarding, custom nftables rules, protection modules, a theft-proof audit log. No cloud, no account, no telemetry you did not agree to.
- Ports — single or range, with per-rule SSH brute-force routing
- Blocklist & allowlist — IPv4, IPv6, CIDR, evaluated before any port rule
- Port forwarding — NAT redirects with protocol selection
- Custom rules — raw nftables, syntax-checked before it is ever applied
- Docker coexistence — owns
table inet easywall, touches nothing else - English, Deutsch and Français, light & dark
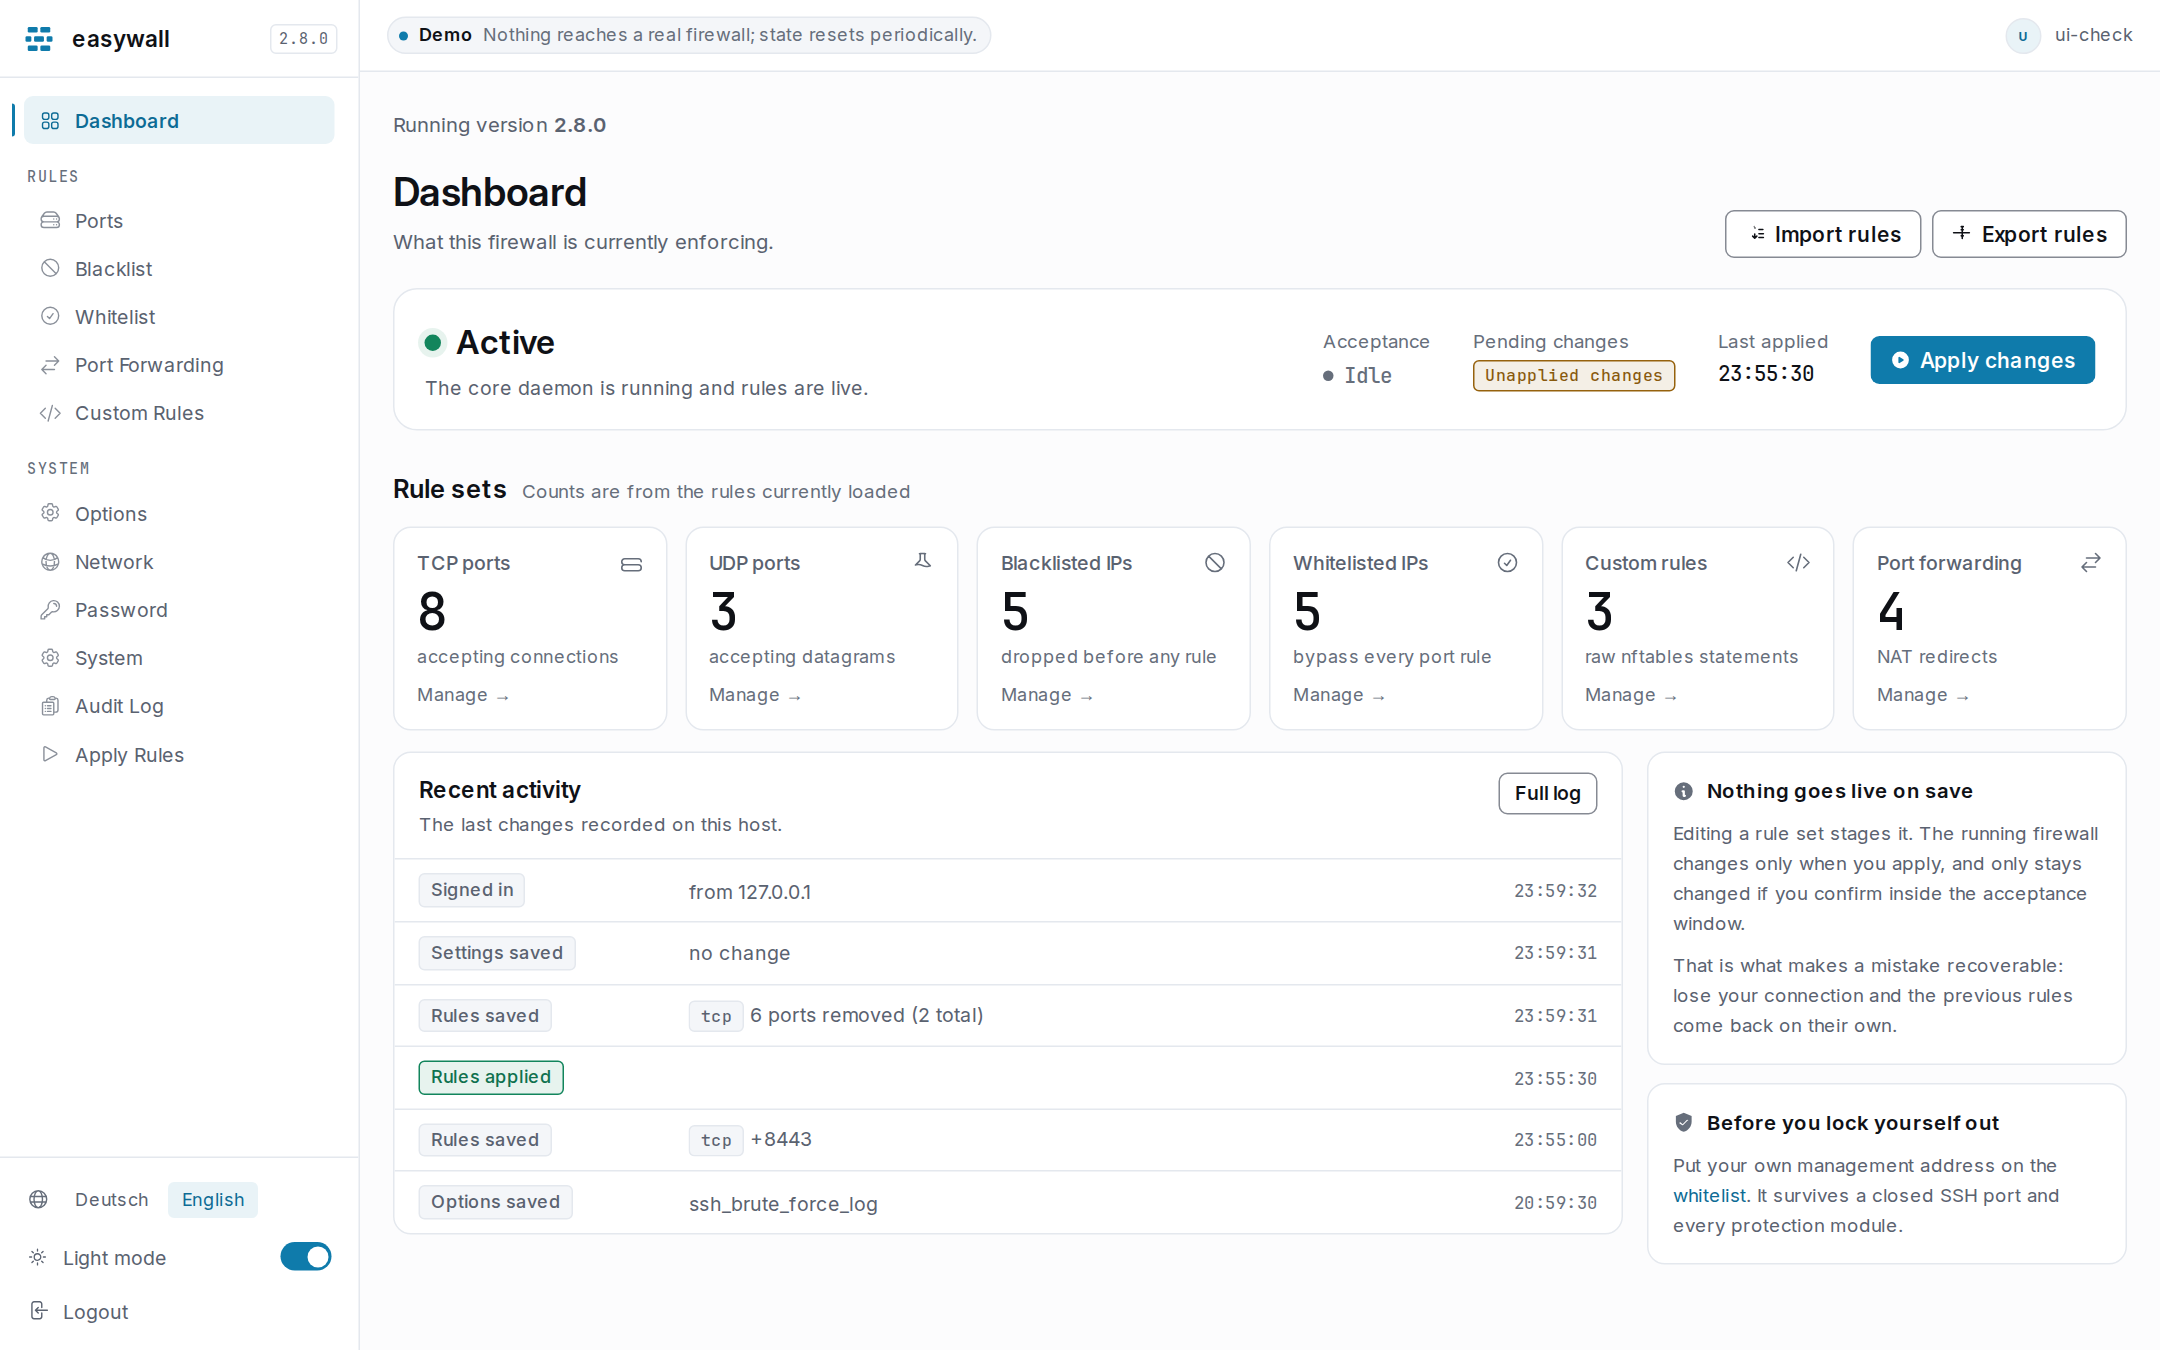
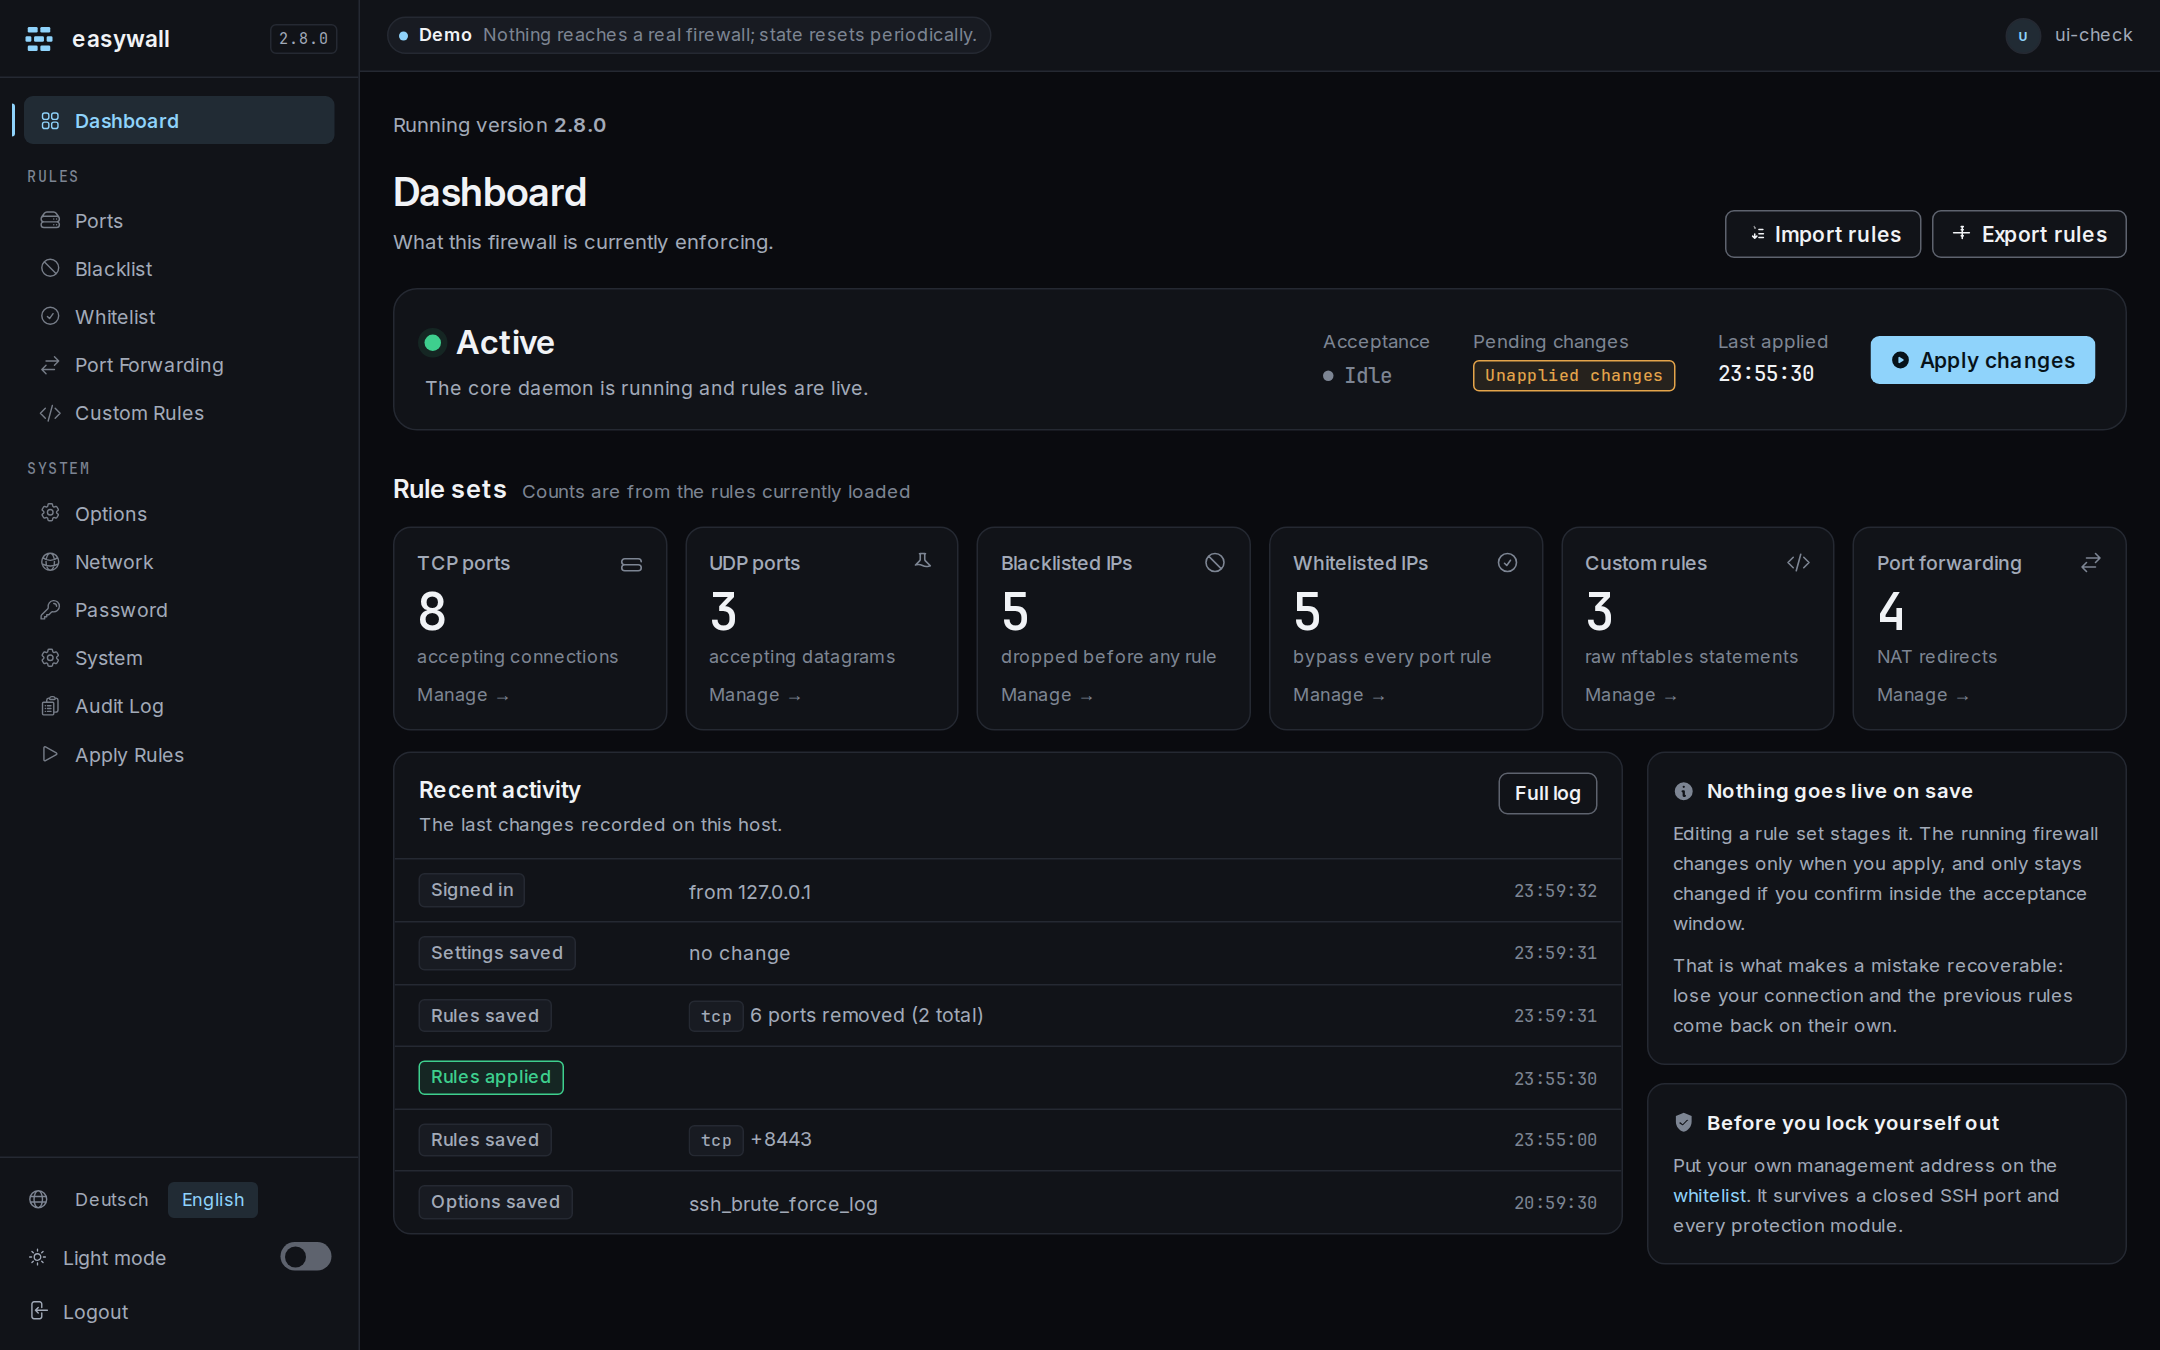
Try it before you install it
A full interface running against an in-memory mock. Nothing reaches a real firewall.
No account needed: one button takes you in.
Built as open source, for 2026
Go, GPL-3.0, nftables via netlink. The apply can never lock you out. Take a look at the architecture and the security model. Find us on Discord and GitHub.